IT Security Solutions for Business: Protect Your Data & Prevent Breaches
Imagine walking into your office Monday morning to find your entire customer database gone, replaced by a digital ransom note demanding payment in untraceable cryptocurrency. Your business operations have ground to a halt. You can’t process orders, you can’t contact clients, and your reputation is tanking by the minute. This isn’t a Hollywood movie plot—it’s a daily reality for businesses that treat IT security solutions for business as an afterthought.
In today’s digital-first world, your company’s data is its most valuable asset. Yet many business owners and managers operate under a dangerous misconception: “We’re too small to be a target.” Hackers and cybercriminals don’t discriminate by company size; they look for the easiest entry point. The right IT security solutions for business aren’t just about compliance or checking boxes—they’re your frontline defense against financial loss, operational disruption, and brand damage. This guide will walk you through the essential security layers every business needs, from foundational practices to advanced protections, all explained in practical, actionable terms.
Key Takeaways: What You Need to Know About IT Security Solutions
- Multi-Layered Protection Is Non-Negotiable: Relying on a single tool (like antivirus) leaves massive gaps. Effective security uses overlapping layers—firewalls, endpoint protection, email filtering, and user training—to create a cohesive defense.
- Your Employees Are Your Biggest Vulnerability—and Your Greatest Asset: Over 90% of breaches start with human error, like clicking a phishing link. Comprehensive security includes continuous training to turn your team from a risk into a detection network.
- Proactive Monitoring Beats Reactive Cleanup Every Time: The average cost of a data breach now exceeds $4.45 million. Investing in 24/7 threat detection and managed security services is far cheaper than the aftermath.
- Compliance Doesn’t Equal Security: Meeting GDPR, HIPAA, or PCI DSS requirements is just the baseline. True security goes beyond compliance to anticipate emerging threats and protect your specific business workflows.
- Cloud Services Require a Shared Responsibility Model: Using AWS, Azure, or Google Cloud doesn’t mean they handle security for you. You’re responsible for securing your data within their platforms—a critical distinction many businesses miss.
- Incident Response Planning Is as Important as Prevention: Assume breaches will happen. A tested, documented incident response plan can reduce downtime by over 50% and limit legal and regulatory fallout.
The Modern Threat Landscape: Why Your Business Is a Target
Cybercrime has evolved from teenage hackers in basements to sophisticated, financially-motivated organizations. They use automation to scan millions of businesses for vulnerabilities, targeting everything from your accounting software to your smart office thermostat. Small and medium businesses are particularly attractive because they often have valuable data (customer information, payment details, intellectual property) but lack the robust security budgets of large corporations.
Beyond Ransomware: The Full Spectrum of Business Threats
Ransomware grabs headlines, but it’s just one tool in the attacker’s arsenal. Business Email Compromise (BEC) scams trick employees into wiring money to fraudulent accounts, costing businesses billions annually. Supply chain attacks infiltr through your vendors’ weaker security. Credential stuffing uses leaked passwords from other breaches to access your systems. Without comprehensive IT security solutions for business, you’re essentially leaving your digital doors unlocked with a neon “Welcome” sign.
Editorial Insight: “The most dangerous myth in cybersecurity is the belief that you’re not a target. Modern attackers don’t hunt specific companies; they cast wide nets using automated tools. Your business gets caught in that net not because of who you are, but because of what you lack—proper security controls. The question isn’t ‘if’ you’ll be attacked, but ‘when’ and ‘how well you’ll withstand it.'”
Essential IT Security Solutions Every Business Should Implement
Building a resilient security posture starts with foundational elements, then adds specialized layers based on your industry, data sensitivity, and risk tolerance. Think of it as constructing a house: you need walls and a roof before installing a security system.
Endpoint Protection: Securing Every Device
Every laptop, desktop, smartphone, and tablet that connects to your network is an endpoint—and a potential entry point. Modern endpoint protection goes far beyond traditional antivirus. Look for solutions that include:
- Behavioral Analysis: Detects malicious activity based on how software acts, not just known virus signatures.
- Device Control: Manages what USB devices, external drives, and peripherals can connect to company machines.
- Application Whitelisting/Blacklisting: Controls which programs can run on business devices.
Network Security: Your Digital Perimeter
Your network is the highway connecting all your business operations. Next-generation firewalls (NGFWs) provide intelligent traffic filtering that understands the context of data flows—not just blocking ports but analyzing what’s actually traveling through them. Combine this with intrusion prevention systems (IPS) that detect and block attack patterns in real-time, and Secure Web Gateways (SWG) that filter malicious websites and content.
Email Security: The Human Firewall
Email remains the #1 attack vector. Advanced email security solutions use AI to detect sophisticated phishing attempts that bypass traditional spam filters. They scan attachments in sandboxed environments before delivery, check links against real-time threat databases, and can even detect impersonation attempts where attackers spoof executive email addresses to request urgent wire transfers.
Identity and Access Management (IAM)
Who has access to what? IAM solutions ensure employees only access systems and data necessary for their roles (the principle of least privilege). Multi-factor authentication (MFA) adds an essential second layer—requiring something you know (password) plus something you have (phone app notification) or something you are (fingerprint). Without MFA, a single stolen password can grant attackers full access.
Comparing Popular IT Security Solutions for Business
| Solution Type | Best For | Key Features | Typical Price Range | Common Limitation |
|---|---|---|---|---|
| Unified Threat Management (UTM) | Small businesses needing all-in-one protection | Firewall, VPN, antivirus, content filtering in single appliance | $500-$3,000/year | Can become bottleneck as business scales; may lack advanced features |
| Endpoint Detection & Response (EDR) | Companies with remote/mobile workforce | Real-time monitoring, threat hunting, forensic analysis on devices | $30-$100/device/year | Requires skilled staff to interpret alerts; can be resource-intensive |
| Cloud Access Security Broker (CASB) | Businesses heavily using SaaS applications (Office 365, Salesforce, etc.) | Visibility into cloud usage, data loss prevention, compliance monitoring | $10-$25/user/month | Primarily cloud-focused; doesn’t replace on-premise security |
| Managed Security Service Provider (MSSP) | Companies lacking in-house security expertise | 24/7 monitoring, threat intelligence, incident response, managed firewalls/EDR | $2,000-$10,000+/month | Less direct control; quality varies significantly between providers |
Deep Dive: Two Critical Security Approaches
Zero Trust Architecture
Forget the old “trust but verify” model. Zero Trust operates on “never trust, always verify.” It assumes threats exist both outside and inside your network. Every access request—whether from an employee on the corporate Wi-Fi or a contractor accessing a cloud app—is authenticated, authorized, and encrypted. Micro-segmentation breaks your network into tiny zones, so a breach in marketing doesn’t automatically spread to finance or R&D. While implementation can be complex, it’s becoming the gold standard for businesses handling sensitive data.
Security Awareness Training Platforms
Technology alone can’t stop phishing emails that mimic your CEO’s writing style or urgent invoices from “vendors.” Modern training platforms use simulated attacks—fake phishing emails, social engineering calls—to teach employees through experience rather than boring slideshows. The best platforms provide personalized coaching based on which traps an employee falls for, turning your human layer from liability to strength. Metrics show businesses with ongoing training programs reduce phishing susceptibility by over 70%.
Common IT Security Mistakes Businesses Make
- Treating Security as a One-Time Project: Installing a firewall and calling it done. Security is an ongoing process requiring continuous monitoring, updating, and adaptation to new threats.
- Neglecting Patch Management: Unpatched software is the most common vulnerability exploited by attackers. Automated patch management ensures critical updates get applied promptly—not “when someone remembers.”
- Granting Excessive Access Privileges: Giving every employee admin rights “to make things easier.” This violates least privilege principles and gives attackers immediate high-level access if they compromise any account.
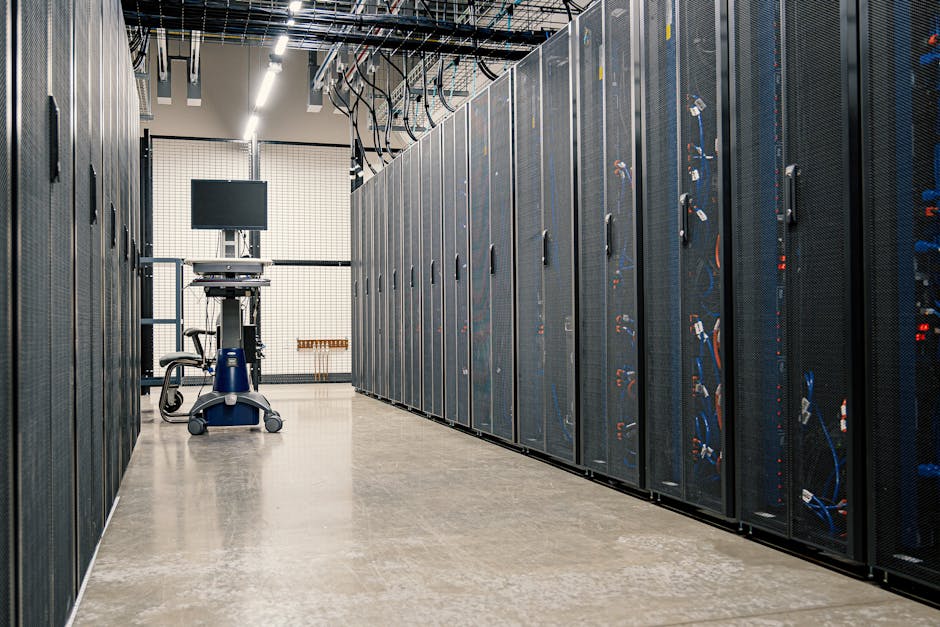
- Ignoring Physical Security: Focusing only on digital threats while leaving servers in unlocked rooms or workstations logged in overnight. Physical access often defeats even the best cybersecurity.
- Having No Documented Incident Response Plan: Winging it during a crisis. A clear plan defines who does what when a breach occurs—containment, communication, recovery—preventing panic-driven decisions that worsen the situation.
- Skipping Regular Security Audits: Assuming everything’s working because you’re not seeing alerts. Regular penetration testing and vulnerability assessments uncover weaknesses before attackers do.
Frequently Asked Questions About IT Security Solutions
What’s the biggest return on investment for IT security spending?
The highest ROI typically comes from layered, fundamental controls rather than exotic tools. Implementing and enforcing Multi-Factor Authentication (MFA) across all business accounts can prevent over 99% of automated attacks targeting credentials. Regular, automated backups stored offline can neutralize ransomware threats—you simply restore from backup instead of paying. Employee security awareness training significantly reduces successful phishing, your most likely attack vector. These foundational elements deliver disproportionate protection relative to their cost.
How do we choose between in-house security staff vs. managed services?
This depends heavily on your business size, industry regulations, and internal expertise. Most small to medium businesses benefit from a hybrid approach: an internal person managing vendor relationships and day-to-day operations, complemented by a Managed Security Service Provider (MSSP) for 24/7 monitoring, threat intelligence, and incident response. This gives you both control and access to specialized skills that would be prohibitively expensive to hire full-time. For highly regulated industries (finance, healthcare), more in-house oversight is often necessary.
Can’t we just rely on our cloud provider’s security?
This is a dangerous misconception. Cloud providers like AWS, Microsoft Azure, and Google Cloud operate on a “shared responsibility model.” They secure the infrastructure—the physical data centers, servers, and network hardware. You’re responsible for securing your data and applications within that infrastructure—configuring access controls, encrypting sensitive information, managing user identities. Many devastating cloud breaches occur because businesses misunderstood this division, leaving sensitive databases exposed to the public internet with default settings.
How often should we update our security policies and solutions?
Policies should be living documents reviewed at least quarterly, with a comprehensive annual overhaul. The threat landscape changes too rapidly for yearly reviews to suffice. Technical solutions require continuous attention: critical patches within days of release, monthly reviews of security tool configurations, and quarterly assessments of whether your current tools still match your evolving business needs. The most secure businesses treat security as a core business process with regular checkpoints, not a “set and forget” technology installation.
What’s the single most important thing we can do right now?
If you’re starting from scratch, enable Multi-Factor Authentication (MFA) on every business account that offers it—especially email, banking, cloud storage, and administrative systems. Email is particularly critical because compromising an executive’s email can facilitate financial fraud, data theft, and further attacks on your partners. Next, implement a regular, automated backup regimen with at least one set of backups stored offline (air-gapped) to protect against ransomware. These two steps alone will dramatically raise your security baseline while you work on more comprehensive IT security solutions for business.
How do we measure the effectiveness of our security solutions?
Look beyond “no breaches” as your only metric. Track measurable indicators: mean time to detect threats, mean time to respond, percentage of employees failing phishing tests, number of unpatched critical vulnerabilities, coverage of MFA across user accounts, frequency of security training completion. Regular penetration tests (at least annually) provide an external assessment of your defenses. The goal isn’t perfection—that’s impossible—but demonstrable improvement over time and visibility into where your remaining risks lie.
Conclusion: Building a Culture of Security
Effective IT security solutions for business aren’t just about buying the right software or appliances. They’re about creating a culture where security is everyone’s responsibility—from the CEO questioning whether a vendor’s data practices are secure enough, to the newest intern thinking twice before clicking an unexpected link. Start with the fundamentals: strong authentication, regular backups, employee education, and basic network protections. Then, layer on more advanced solutions based on your specific risks and regulatory requirements. Remember, the cost of prevention is always lower than the cost of a breach—not just in direct financial terms, but in lost customer trust, operational disruption, and competitive disadvantage. Your business’s resilience depends on the security foundations you build today.